 AttestOS
Let real people in, without making them prove it.
Every puzzle on your sign-up form loses some of the people who were ready to say yes. AttestOS replaces image puzzles on sign-up, login and contact forms with a small proof-of-work check that runs in the background, plus a server-side verify call shaped like reCAPTCHA's. Real people just submit the form.
10,000 verifications a month free · one script tag + one API call · works with any backend
Try it: this form is protected
Your browser is solving a small challenge now. Submitting sends the token to our "backend", which calls /api/siteverify:
{ "waiting": "submit the form" }Sound familiar?
Product and growth teams
Someone on a phone, on a slow connection, gets the traffic-light puzzle wrong twice and closes the tab. You paid to bring them there.
With AttestOS: the check runs quietly while they type. They press the button and they are in.
Get a free site keyWhoever owns the login page
A Monday morning of fake accounts and password-stuffing attempts, and a CAPTCHA that annoys customers more than it slows the attackers.
With AttestOS: every automated attempt costs the attacker compute, tokens are single-use and domain-bound, and Pro shows you how risky each solve was.
Scan your login pagePublishers and documentation sites
AI crawlers read everything you wrote, every day, and you were never asked.
With AgentPass: you decide per crawler: allow it, block it, or answer with your own payment link. Your work, your terms.
See AgentPassHow it works
The page solves
Our widget fetches a signed challenge and finds a nonce whose SHA-256 has enough leading zero bits. That takes a browser a fraction of a second; doing it millions of times costs a bot farm real compute.
The form carries a token
The solution is exchanged for a pass token that lives 5 minutes and is bound to your site key and domain. It lands in a hidden field, attestos-response.
Your server verifies once
Your backend posts the token and your secret key to /api/siteverify. The first call succeeds; any replay fails with timeout-or-duplicate.
<script src="https://attestos-edge.proofhand.workers.dev/v1/attestos.js" async defer></script>
<form method="post" action="/signup">
  …
  <div class="attestos" data-sitekey="ao_site_…"></div>
  <button>Sign up</button>
</form>
// your backend (Node 18+)
const r = await fetch("https://attestos-edge.proofhand.workers.dev/api/siteverify", {
method: "POST",
headers: { "content-type": "application/json" },
body: JSON.stringify({ secret: process.env.ATTESTOS_SECRET,
response: req.body["attestos-response"] }),
});
const v = await r.json(); // { success: true, hostname, method, … }
if (!v.success) return res.status(400).send("Bot check failed");One free core, four paid modules
Every plan includes the free core. Paid plans are monthly on Whop and can be combined.
 Free
Ghost-PoW core
Bots stopped, and real people never see a puzzle.
Invisible proof-of-work widget, server-side verify with single-use tokens, domain lock, an AI-crawler rule check, and passkeys for up to 50 users.
 $49/mo
IntegrityRuntime Pro
Know how risky every solve was, and tighten only when it matters.
Automation signals (webdriver flag, headless user agents, software GPU, native-speed solvers…) turned into a risk score in every verify response, adaptive difficulty during surges, Slack/Discord alerts, audit export.
 $149/mo
Hardware Gateway Pro
Trusted devices walk straight in. Everyone else still gets through.
Private Access Tokens (Privacy Pass, RFC 9576–9578): supporting Apple devices skip the solve entirely, everyone else falls back to Ghost-PoW. Plus unlimited passkeys.
 $99/mo
AgentPass Pro
AI crawlers either pay you or stay out.
Decide per AI crawler: allow, block, or answer HTTP 402 with your own payment link. Crawler claims are checked against the operators' published IP ranges. Sell metered agent keys.
 $299/mo
Enterprise
Everything, at a size where you stop thinking about limits.
All modules, 300,000 verifications a month, 25 sites.
Not sure yet?
Run the free scanner on your sign-up page. It shows which CAPTCHA (if any) you run today, how your robots.txt treats AI crawlers and which security headers are missing.
Open the scanner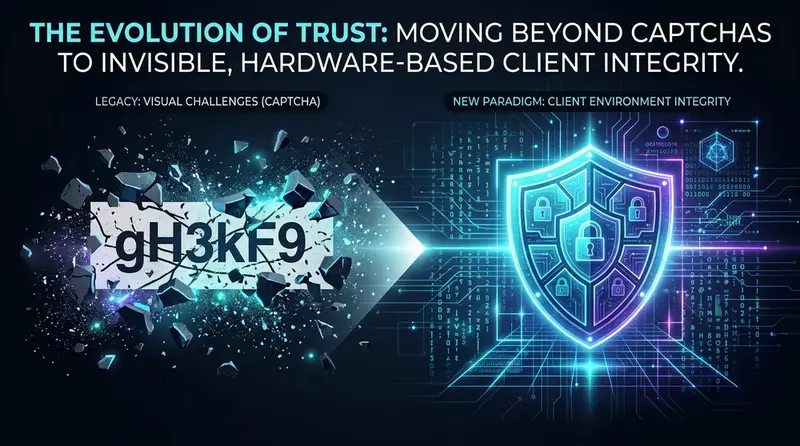
What proof-of-work does, honestly
- Makes every automated submission cost CPU time, which kills cheap mass sign-ups, credential stuffing at scale and form spam floods.
- Asks nothing of real visitors: no puzzles, no clicks, no third-party tracking cookies.
- Single-use, short-lived, domain-bound tokens: a solved token can't be farmed and replayed.
- It is not identity. A patient attacker with real compute can still pay the price, so keep server-side rate limits, and add the risk score or passkeys where it matters.
- No tool can promise zero bots. We report what we check, and the verify response tells you how a token was earned.
Questions
Does it replace reCAPTCHA v2 / hCaptcha one to one?
Yes for the integration shape: a script, a hidden field and a siteverify call with success, challenge_ts, hostname and error-codes. The difference is that visitors see nothing.
What happens if AttestOS is down or my quota runs out?
You decide. The docs show a fail-open pattern for quota-exceeded and network errors, so your sign-ups never stop because of us.
Is visitor data sent anywhere?
The challenge is served from Cloudflare's edge. On paid IntegrityRuntime plans the widget also sends a few browser facts (listed in the privacy policy) to compute the risk score. No cookies, no cross-site tracking.
How do I pay?
Checkout runs on Whop. Buy with the same email as your AttestOS account and the plan attaches automatically once your email is confirmed.